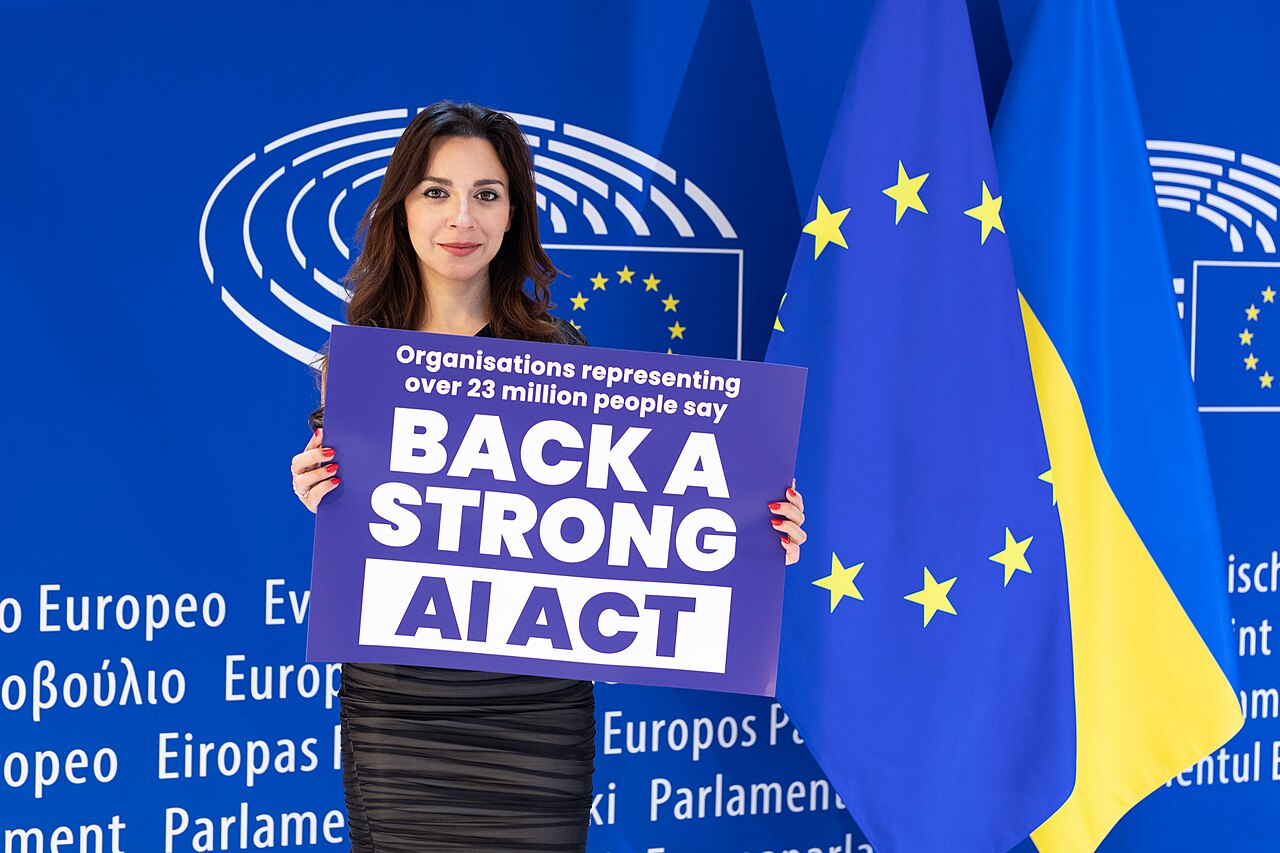
Commentary. Europe is right to ask whether its artificial-intelligence rulebook has become unnecessarily difficult to apply. It would be wrong, however, to confuse simplification with progress. The test of the EU’s new approach should not be whether companies face fewer forms. It should be whether people remain protected when automated systems influence employment, credit, health care, education or public services.
The European Parliament and Council adopted the Digital Omnibus on AI in July, amending the bloc’s AI Act and related legislation in the name of simpler implementation. The regulation entered into force shortly after publication and is directly applicable across member states, according to the official EU text.[1] That is a significant development: after years of presenting the AI Act as a global regulatory model, Brussels is acknowledging that compliance can be technically and administratively burdensome.
Our view is that this correction is necessary—but should remain narrowly targeted. Rules that eliminate duplication, clarify timelines or align overlapping obligations can help smaller companies compete and make enforcement more predictable. Rules that quietly reduce documentation, testing or transparency would be a different matter. In high-impact applications, paperwork is not the objective, but it is often the evidence that a provider considered foreseeable risks before deployment.
The case for simplification
Businesses have legitimate complaints. AI developers operate across borders, while obligations can be scattered among product safety, data protection, cybersecurity and sector-specific regimes. A start-up may lack the legal teams available to a multinational, yet face uncertainty over which requirements apply to a general-purpose model or a system embedded in another product.
That uncertainty can delay useful tools in medicine, research and accessibility. It can also encourage companies to launch first and interpret the law later. A clear, proportionate framework is more likely to produce compliance than a maze of overlapping duties. The EU’s amendment therefore deserves more than reflexive opposition: a regulation that cannot be understood by those expected to follow it will not protect the public effectively.
Why caution is warranted
The counterargument is equally strong. AI risks do not disappear because compliance is inconvenient. Automated systems can reproduce discrimination, expose sensitive information or make errors at a scale that conventional software cannot. The people affected often have little ability to inspect a model, challenge its output or obtain compensation.
Recent international policy developments underscore the broader concern. Singapore’s monetary authority issued final AI-risk-management guidelines for financial institutions in October, setting supervisory expectations for firms adopting AI, according to a regulatory briefing reported by Bloomberg.[2] The direction of travel is clear: responsible deployment requires governance, testing and accountability, not merely innovation-friendly language.
There is also a democratic issue. Regulators should not measure success only by the number of obligations removed. They should disclose which safeguards are being changed, why the change is justified and what evidence will show that it has not increased harm. Public trust depends on that chain of explanation.
A better standard
Europe should simplify the path to compliance while preserving the substance of protection. That means standardized templates, shared testing tools, practical guidance for small firms and a single portal for reporting. It means allowing equivalent safeguards rather than demanding identical procedures. But it also means retaining independent assessment for genuinely high-risk uses, meaningful records of training and testing, and accessible routes for people to contest consequential decisions.
The same principle should guide national authorities. Enforcement should focus scarce resources on systems with power over people’s opportunities and rights, rather than treating every experimental application as equally dangerous. A low-risk productivity tool and an automated system screening job applicants should not face the same burden.
Critics of regulation will say Europe risks falling behind the United States and China. That warning should be taken seriously. Excessive friction can push investment elsewhere, and fragmented enforcement can punish compliant firms while rewarding those willing to gamble. But the answer is not a race to the bottom. Clear rules can become a competitive advantage if they make trustworthy products easier to buy, deploy and scale.
The EU’s AI simplification effort is therefore worth supporting—but only as administrative reform, not as a retreat from accountability. Europe should make compliance cheaper, clearer and more consistent. It should not make the public responsible for discovering, after deployment, which safeguards were deemed too inconvenient to keep.