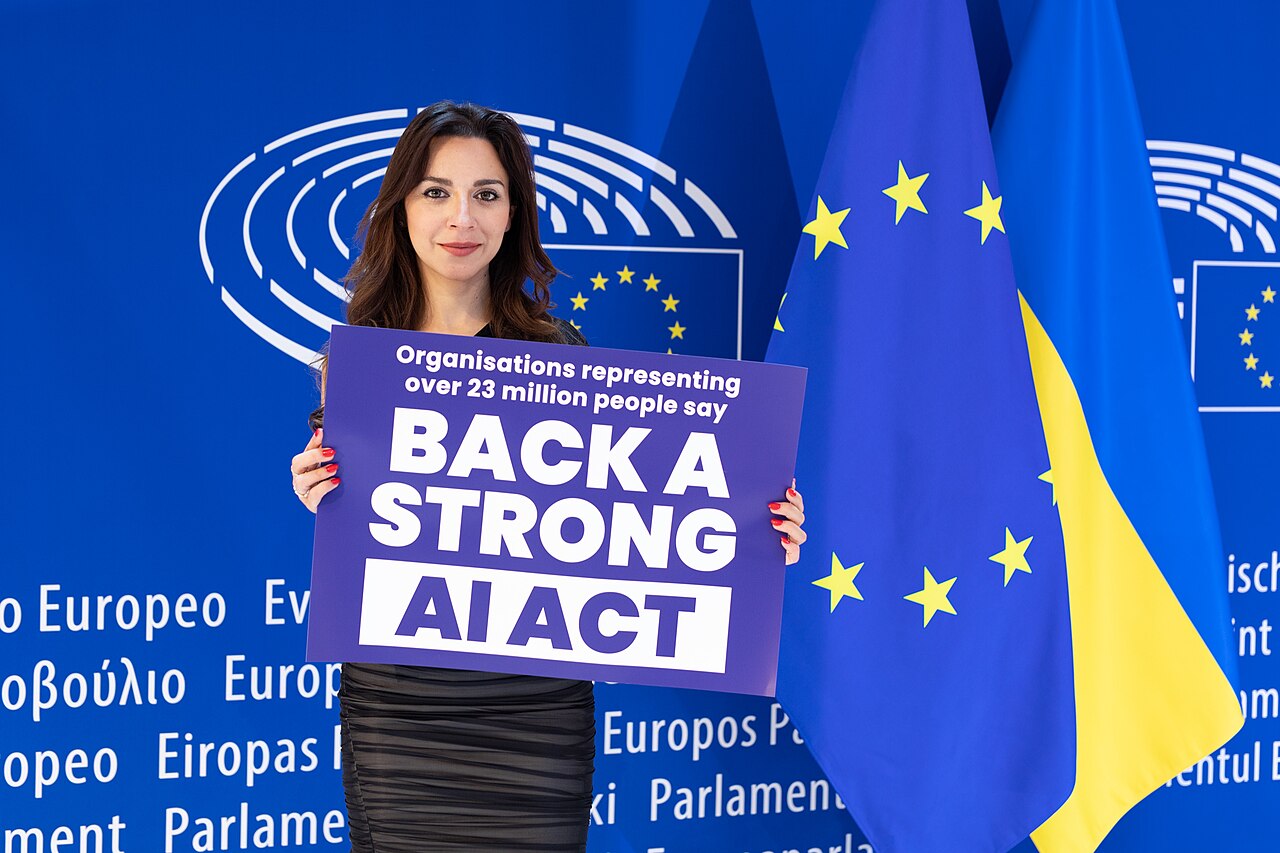
Commentary. Artificial-intelligence policy has reached the point where delay is no longer neutral. Automated systems already influence employment, housing, finance and education, while conversational tools increasingly shape how people seek information and make decisions. The question is not whether governments should regulate AI, but whether they can do so without turning every new application into a compliance maze.
Our view is that they should pursue firm, targeted rules: transparency when automated systems affect people’s opportunities; meaningful human review; independent testing for high-risk tools; and stronger protections for children. Regulation should focus on consequences, not on the novelty of the technology itself.
That approach is becoming more plausible in the United States. The 2026 legislative session has produced AI bills addressing automated decision-making, frontier-model risks, third-party auditing and public-sector use. According to the Center for Democracy & Technology, 69 bills had been introduced across 26 states, with measures passed in Maryland, Minnesota and New York; Connecticut enacted what the organization described as the session’s most comprehensive law.[1]
The spread of state legislation reflects a legitimate democratic response to federal inaction. The same review found that no federal AI bill had passed during the current session.[1] Waiting for a single national framework may sound orderly, but it leaves workers, consumers and students navigating a patchwork of protections—or none at all.
Still, the patchwork has real costs. Companies operating across state lines may face conflicting definitions, reporting duties and liability standards. Smaller firms could struggle to hire lawyers and auditors, reducing competition while leaving the largest technology companies best equipped to absorb compliance expenses. Colorado’s decision to rescind and replace its landmark automated-decision regulation is a reminder that ambitious rules can be revised when lawmakers judge them impractical or poorly calibrated.[1]
The answer is not deregulation by exhaustion. It is disciplined legislation. Rules should distinguish between a recommendation engine that sorts low-stakes content and a system that helps determine whether someone gets a job, a mortgage or admission to an educational program. The latter deserves evidence of accuracy, bias testing, records of use and a route for appeal. A company should not be allowed to hide a consequential decision behind the phrase “the algorithm did it.”
The case for restraint
Critics of tougher oversight make two serious arguments. First, AI is developing faster than conventional rulemaking. Prescriptive requirements could lock in today’s technical assumptions and make it harder for smaller innovators to compete. Second, many harms attributed to AI—discrimination, manipulation and opaque corporate decision-making—also existed before machine learning. Poorly drafted legislation may punish a tool rather than address the institution deploying it.
Those objections deserve more than a passing acknowledgment. A regulator that demands impossible guarantees will encourage superficial paperwork, not safer systems. And rules should not exempt human decision-makers from scrutiny while imposing extraordinary burdens on software. Accountability must follow the decision and its impact, whether the final input comes from a manager, a model or both.
Europe offers a different model. Its AI Act uses a risk-based framework, with stricter obligations for high-risk systems, including tools used in recruitment and worker management.[2] The framework’s staged implementation shows both the value and the difficulty of comprehensive regulation: clear categories can establish expectations, but deadlines and obligations must remain workable as technical practice changes.
The European Union is also preparing rules on algorithmic management through its Platform Work Directive, including transparency, human oversight and information rights for workers’ representatives.[2] That emphasis is welcome. People affected by automated management need more than a privacy notice; they need to know when a system evaluates them, what data matters and how to contest an outcome.
Our editorial position is therefore neither “regulate everything” nor “let the market decide.” Governments should prohibit clearly abusive uses, impose auditable duties on high-impact systems and require accessible remedies. They should coordinate standards across jurisdictions, fund public-interest testing and review rules on a fixed schedule. Companies, for their part, should stop treating transparency as a public-relations exercise and publish enough information for independent scrutiny.
AI may produce large gains in medicine, research, accessibility and productivity. Those gains are not secured by trusting technology blindly. They are secured when the public can see where power is exercised, challenge mistakes and believe that innovation serves people rather than merely outruns them.