Commentary. Artificial intelligence policy is entering its most consequential phase: governments are no longer debating whether rules are necessary, but how quickly they should take effect and how much authority regulators should have. Our view is straightforward: lawmakers should regulate demonstrable harms now, while resisting the temptation to govern every future possibility through sprawling, incompatible rulebooks.
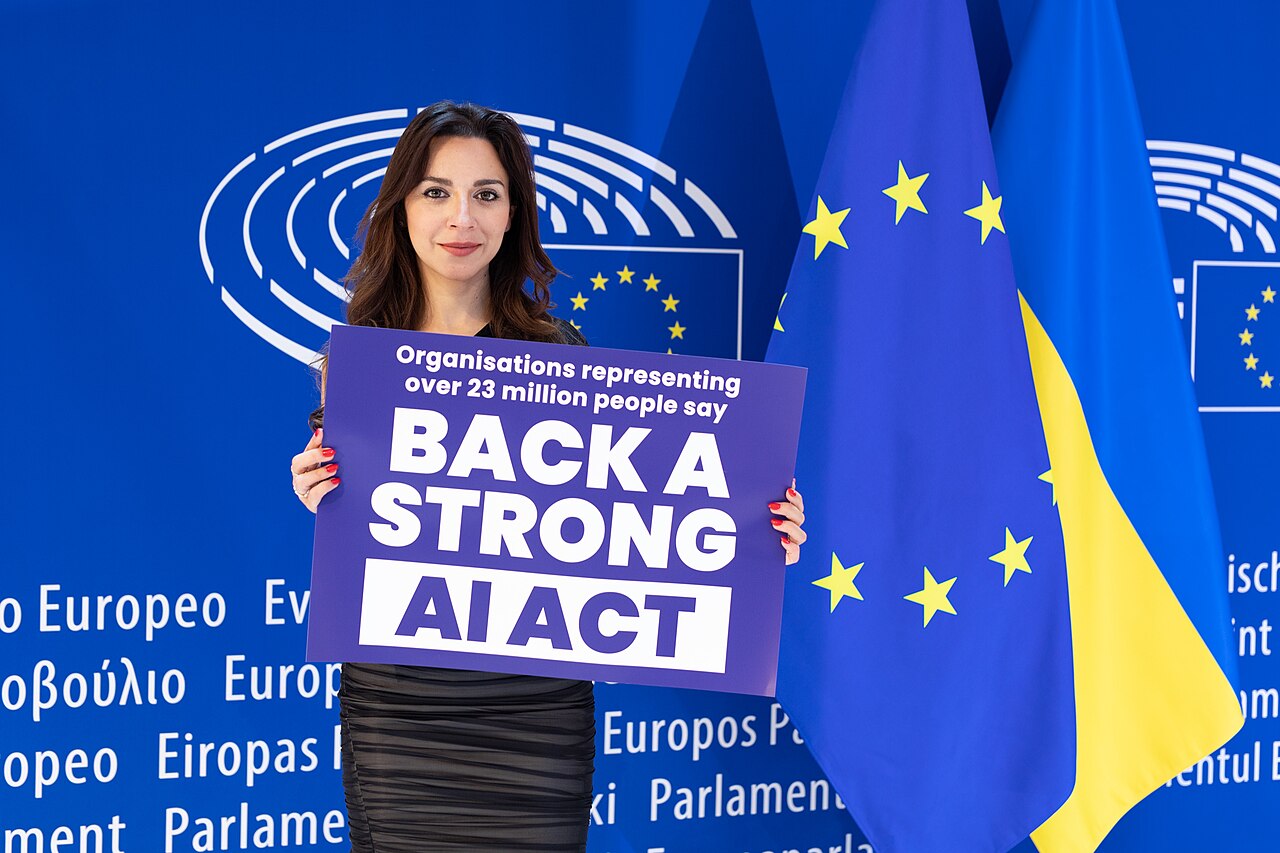
Recent developments illustrate both the urgency and the danger. The European Union’s revised AI framework sets new deadlines for high-risk systems, including stand-alone applications and systems embedded in products. It also adds a prohibition on generating non-consensual intimate or sexual content and child sexual abuse material, while postponing some obligations for labeling AI-generated content. The final agreement was approved by the European Parliament and Council in 2026 and published in the EU’s Official Journal in July. European Parliament
That combination—stronger prohibitions alongside delayed compliance deadlines—captures the policy dilemma. The public deserves protection from clearly abusive uses of AI. But companies, universities and public agencies also need workable timelines, technical standards and a stable understanding of what compliance means. Rules that arrive before guidance, testing capacity or qualified auditors risk producing paperwork rather than safety.
The case for stronger oversight
The argument for regulation is not theoretical. AI systems can influence employment, health care, education, policing and access to essential services. Errors in these settings can affect people who never chose to interact with a model and may have no practical way to challenge its output. Transparency, impact assessments, human oversight and incident reporting are therefore reasonable baseline requirements—not bureaucratic luxuries.
Proposed measures in India’s telecom sector point in that direction. Draft guidelines would require operators using AI to maintain board-approved policies, classify systems by risk, establish governance committees, conduct impact assessments and report serious incidents. The proposal also invites public comment, a useful reminder that implementation should be tested in the open rather than imposed as a finished theory. Economic Times
There is also a compelling case for targeted protections for children. New York has enacted restrictions on AI companion chatbots that appear human, encourage emotional dependence or promote self-harm and eating disorders, according to a policy update summarizing the law. a16z Policy Such rules raise difficult questions about definitions and enforcement, but the underlying concern is legitimate: a conversational system designed to maximize engagement should not be treated like a neutral search box when minors are involved.
The cost of fragmentation
Yet every new obligation carries costs. Smaller developers may lack the legal and engineering teams needed to comply with multiple national regimes. Public-interest researchers can be trapped by unclear rules around data, model access and testing. Large technology companies, by contrast, may absorb compliance expenses and use complexity to reinforce their market position. Regulation meant to curb concentration could unintentionally deepen it.
Fragmentation also creates a security problem. A model may be trained in one country, hosted in another and deployed through a service operating across dozens of jurisdictions. Divergent definitions of risk and inconsistent reporting requirements make it harder to compare incidents or respond quickly. A company can satisfy the letter of one rule while evading the spirit of another.
Industry critics are right to warn against premature prescriptive regulation. AI capabilities are changing faster than legislative cycles, and broad restrictions can lock in assumptions that soon become obsolete. Policymakers should not prohibit a technology merely because its risks are unfamiliar, nor should they demand perfect explainability where a system’s performance can be independently tested and bounded.
A practical compromise
The answer is neither laissez-faire nor maximal control. Governments should begin with a narrow set of enforceable duties: disclose meaningful limitations, preserve audit trails, provide remedies for consequential errors, protect personal data, and impose strict prohibitions on clearly abusive content and conduct. Requirements should scale with risk, not with the novelty of the software.
Regulators should also coordinate on testing methods, incident taxonomies and documentation templates. International alignment will not eliminate political differences, but it can prevent every jurisdiction from inventing a separate compliance language. Sunset clauses and mandatory reviews would allow rules to change as evidence accumulates.
Our editorial position is therefore firm but limited: AI governance should be judged by whether it reduces real-world harm, not by the volume of new obligations. The public needs enforceable rights and accountable institutions. Innovators need predictable rules and room to experiment safely. The best policy can provide both—if lawmakers resist the easy politics of announcing control and do the harder work of making oversight function.