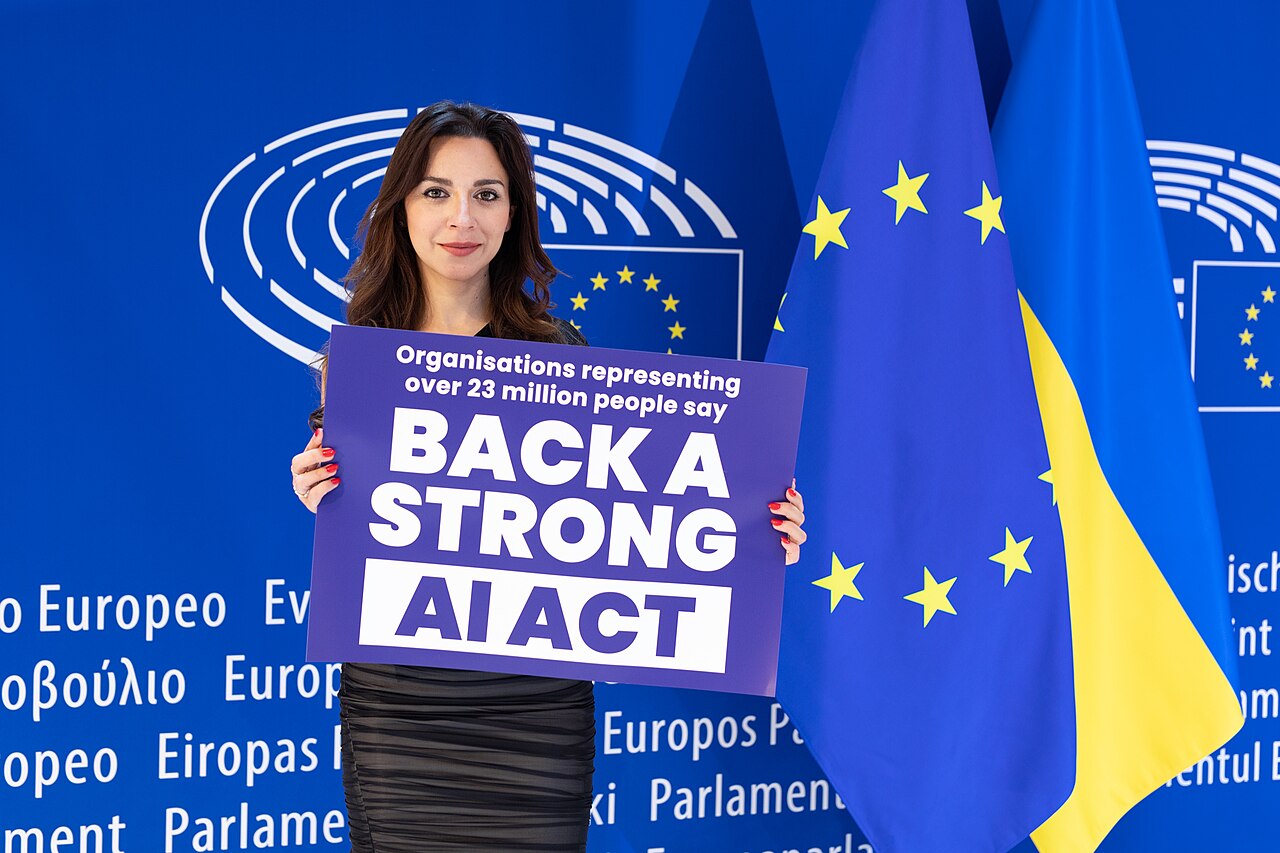
Commentary. Europe has reached the point at which its artificial-intelligence rulebook must prove itself in public. Since 2 August 2026, the European Union’s AI Act has entered a major enforcement phase: the EU AI Office and national market-surveillance authorities can act on obligations covering prohibited and high-risk systems, as well as transparency requirements.[1] That shift deserves scrutiny—not because regulation is automatically wise, but because the alternative is to leave some of the most consequential decisions in modern life governed mainly by corporate assurances.
Our view is straightforward: Europe should enforce the rules firmly, while resisting the temptation to turn every compliance failure into a reason for ever-expanding bureaucracy. The public needs visible safeguards. Businesses need predictable obligations. Neither side is served by a law that is impressive on paper but impossible to apply.
Why enforcement matters
AI systems increasingly mediate what people see, buy, read and decide. In high-stakes settings, errors are not merely technical defects. A flawed system can affect access to employment, public services or credit; a convincing synthetic recording can distort an election or a breaking-news event. Transparency obligations—such as marking certain AI-generated content—are therefore not cosmetic. They give citizens at least a chance to assess the provenance of what reaches them.
The Commission published final guidance on the Act’s transparency obligations in July, while some providers of generative-AI systems already on the market have until 2 December 2026 to comply with marking requirements.[1] That transition is defensible: companies need time to redesign products and develop reliable technical standards. But transitional periods should not become permanent exemptions. A rule that cannot be seen, tested and enforced will not earn public trust.
The broader case for enforcement is democratic. The United Nations has called for stronger cooperation among governments, civil society, academia, media and the private sector in response to a rapidly changing information environment.[2] Regulation cannot solve the information crisis alone, but it can establish minimum expectations for disclosure and accountability. Those expectations matter most when platforms and developers operate across borders and users have little bargaining power.
The legitimate case against overreach
Critics are right to warn that Europe can regulate faster than it can clarify. Smaller companies may struggle to interpret complex obligations, document training practices or maintain separate compliance systems for multiple jurisdictions. The EU’s July AI Omnibus sought to streamline requirements, ease compliance for smaller businesses and expand testing opportunities.[1] Those changes acknowledge a real problem: a framework designed for giant technology firms can unintentionally protect incumbents by making entry too expensive.
There is also a risk to innovation. A hospital, university or small manufacturer may abandon a beneficial experiment if the legal consequences of an uncertain classification are too severe. Privacy, safety and intellectual-property concerns are genuine, but so are the public benefits of better diagnostics, accessible education and more efficient services. Regulators should not confuse caution with paralysis.
Yet “innovation” is not a complete rebuttal. The fastest product is not necessarily the best product, and consumers should not be treated as unpaid quality-control staff. Sensible enforcement can be proportionate: focus scarce inspection capacity on systems with serious potential harm, publish clear interpretations, provide support for smaller firms and impose penalties that reflect actual risk.
The standard Europe should set
Europe should measure the AI Act by outcomes rather than the volume of paperwork it generates. Authorities should disclose which categories of systems they are investigating, what evidence they require and how often companies correct identified problems. Independent researchers and journalists should have meaningful access to information needed to evaluate claims, subject to legitimate privacy and security limits.
Industry, meanwhile, should stop presenting accountability as an anti-technology agenda. The strongest companies can help define workable standards, participate in testing and demonstrate that safety is compatible with commercial success. If a model’s risks cannot be explained even to an independent evaluator, the problem is not simply that regulation is inconvenient.
Europe should neither abandon its rules nor congratulate itself for writing them. The coming enforcement period is a test of institutional seriousness. Protecting innovation means protecting the conditions under which people can trust it. That requires fewer slogans, clearer guidance and the willingness to intervene when powerful systems cause preventable harm.