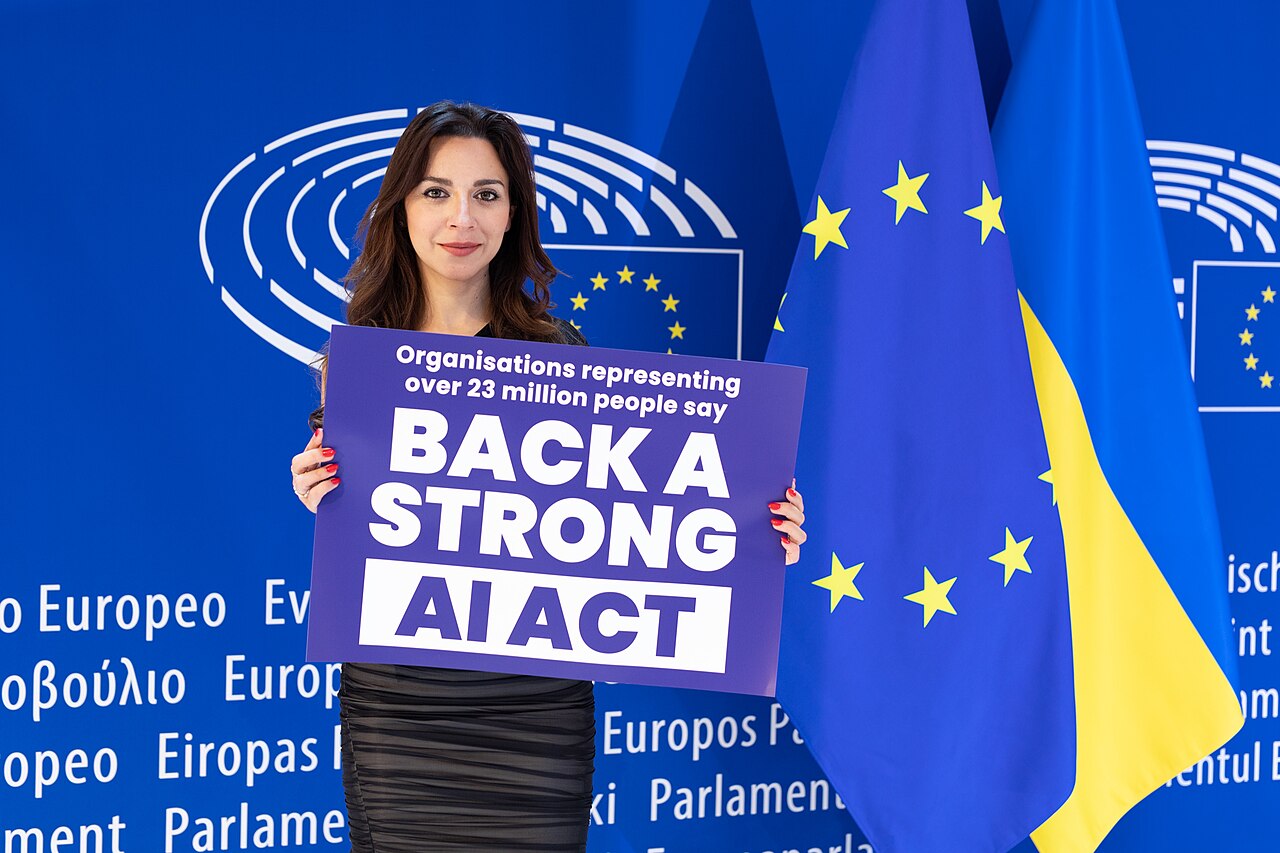
Commentary. The argument over artificial-intelligence regulation has become too binary. One side warns that rules will cripple innovation; the other treats every new safeguard as overdue. Our view is less dramatic and more practical: regulation is necessary, but its success will depend less on the number of obligations than on whether institutions can enforce them consistently.
That test is arriving now in Europe. Transparency obligations under the EU AI Act became applicable on 2 August 2026, giving regulators new powers over disclosure requirements and placing fresh responsibilities on developers and deployers. The framework is also being adjusted through the AI Omnibus, which delays some high-risk-system deadlines while seeking to simplify compliance, particularly for smaller companies. Simmons & Simmons describes the implementation timetable and the changes to the rulebook.
The case for rules
There is a straightforward public interest in requiring people to know when they are interacting with synthetic content or an automated system. AI can influence hiring, access to services, education and personal relationships while remaining opaque to those affected. Disclosure does not solve these risks, but it gives citizens, journalists and regulators a starting point for scrutiny.
Recent US legislative activity reinforces the point that Europe is not alone in confronting these questions. The Center for Democracy and Technology reports that state lawmakers have pursued measures covering chatbots, automated decisions, frontier-model risks, public-sector use and third-party auditing. It also notes that no federal AI bill had passed in the 2026 session at the time of its review. The CDT’s legislative overview details that uneven US approach.
Fragmentation is frustrating, but it also reflects a legitimate democratic concern: different uses carry different risks. A chatbot entertaining a user is not equivalent to software screening applicants for a job. A national security vulnerability tool is not the same as a system generating advertising. One-size-fits-all regulation may be easier to explain, but it is unlikely to be fair.
The case against poorly designed regulation
Critics are right that compliance can impose disproportionate costs. Smaller companies may lack lawyers, testing teams and audit budgets that large technology firms can absorb. Delayed deadlines for high-risk systems acknowledge that regulators and industry need time to produce workable standards. The danger is that uncertainty will deter responsible experimentation while the largest incumbents gain another advantage.
There is also a risk of regulatory theatre. A disclosure label can become a box-ticking exercise if users cannot understand what a system does, what data shaped its output or how to challenge a decision. An audit is valuable only when auditors have access, independence and authority to identify failures. More paperwork is not the same as more accountability.
The uneven US landscape illustrates this problem from another angle. State laws can serve as laboratories, but conflicting definitions and duties may force developers to build for the strictest jurisdiction or abandon smaller markets. Businesses need predictability; the public needs protection. Policymakers should not pretend those goals automatically align.
What enforcement should prioritize
Our editorial position is that governments should focus first on a small set of enforceable guarantees: meaningful notice, records that allow decisions to be reconstructed, independent testing for high-impact systems, and accessible remedies for people harmed by automated decisions. Regulators should publish clear examples, coordinate across borders and measure outcomes rather than merely counting registrations.
They should also resist the temptation to regulate hypothetical catastrophe at the expense of ordinary harms. Frontier-model safety deserves serious attention, including cybersecurity risks. But discrimination in employment, deceptive synthetic media and unsafe systems deployed today are not waiting for a perfect global treaty.
Good AI governance should make responsibility visible: who built the system, who deployed it, who profited from it and who must fix it when it fails.
The strongest objection is that fast-moving technology will outpace legislation. That is true, but it is an argument for adaptable standards, sunset reviews and technically competent regulators—not for leaving citizens to negotiate with companies one complaint at a time.
The EU’s implementation phase should therefore be judged by results. If transparency rules help people detect manipulation and challenge consequential decisions, they will earn public legitimacy. If they create complexity without recourse, critics will rightly call them bureaucratic theatre. The choice is not innovation or regulation. It is whether regulation is designed well enough to make innovation answerable to the people who bear its risks.