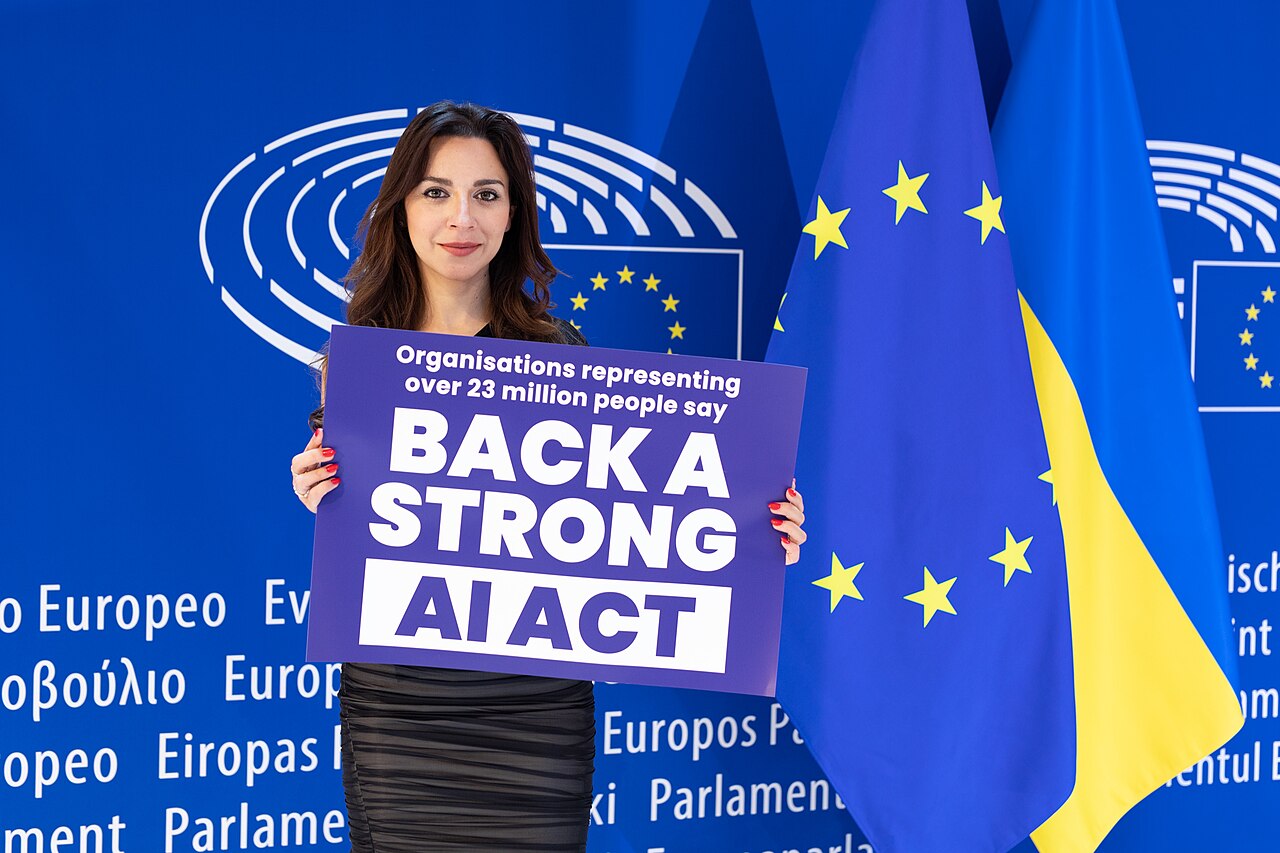
Commentary. Europe has spent years presenting the AI Act as proof that democratic governments can govern artificial intelligence before technology governs them. That claim now faces its first serious test. Since August 2026, the European Commission’s AI Office and national market-surveillance authorities have had enforcement powers under the law, while transparency obligations have begun applying to many AI systems.
Our view is straightforward: Europe should resist the temptation to celebrate the rulebook itself. A regulation is not a safeguard until people can understand it, challenge violations and see consequences for companies that ignore it. The next phase must be about enforcement that is visible, proportionate and technically competent.
The case for firm oversight
The AI Act’s logic is defensible. A chatbot used for entertainment is not equivalent to software influencing employment, access to essential services or other high-stakes decisions. Risk-based regulation can focus scarce public resources where errors carry the greatest human cost, rather than treating every algorithm as equally dangerous.
Transparency is also a modest but necessary starting point. If people are interacting with an AI system or viewing synthetic material, they should not have to guess. The European Commission has published guidance on transparency duties, including obligations connected to identifying certain AI-generated content. Those rules will not eliminate deception, but they can make accountability possible.
Recent developments elsewhere reinforce the need for action. The Bank of England is reviewing whether existing financial regulation can address “agentic” AI in payments, trading, cybersecurity and operations, while the International Monetary Fund’s first deputy managing director has argued that new regulation may be needed for frontier systems. These are not arguments for banning innovation; they are acknowledgements that older supervisory assumptions may no longer fit autonomous or semi-autonomous tools.
The costs of getting it wrong
Still, the strongest case against careless enforcement comes from Europe’s own ambitions. Smaller firms may struggle with documentation, testing and legal uncertainty that larger companies can absorb. Start-ups could delay launches or move research elsewhere, while public bodies might avoid useful systems because compliance appears unpredictable.
Critics also warn that regulation can become technologically obsolete. A detailed obligation written for today’s models may fail to address tomorrow’s systems, encouraging box-ticking rather than genuine risk reduction. Governments that demand disclosure without providing workable technical standards could leave companies guessing and regulators litigating after the harm has occurred.
Those objections deserve more than dismissal. Europe cannot protect citizens by making beneficial applications—such as accessibility tools, scientific assistance or carefully supervised healthcare systems—needlessly expensive. Nor should regulators confuse a model’s novelty with evidence of danger.
What responsible enforcement looks like
The answer is not retreat. It is disciplined implementation. Regulators should publish clear examples of compliant practice, offer rapid guidance to smaller developers and coordinate across borders so the same product does not face contradictory interpretations in different member states. Penalties should target concealment, reckless deployment and repeated non-compliance—not honest mistakes corrected promptly.
Independent auditing must also mean independence. Companies should not be allowed to define safety solely through their own marketing claims, but regulators need access to outside technical expertise rather than relying only on consultants hired by the industry they oversee. Civil-society groups, workers and affected communities should have practical routes to contest automated decisions and obtain human review.
The EU should measure success by outcomes: fewer discriminatory decisions, clearer disclosure, faster remedies and demonstrably safer high-risk systems. The number of guidance documents issued or compliance officers appointed is not the same as public protection.
Europe’s credibility will be determined not by how ambitious its AI law sounds, but by whether an ordinary person can use it when an automated system causes harm.
Innovation and oversight are not natural enemies. Predictable rules can help responsible companies compete by reducing uncertainty and forcing unsafe shortcuts out of the market. But that promise depends on regulators proving that the law is understandable, even-handed and capable of adapting.
Our newsroom’s position is therefore neither “regulate everything” nor “let the market decide.” Europe should enforce the AI Act firmly, revise it when evidence demands, and remain honest about its limits. The public does not need another grand claim that AI is either salvation or catastrophe. It needs institutions strong enough to demand evidence before deployment—and remedies when promises fail.