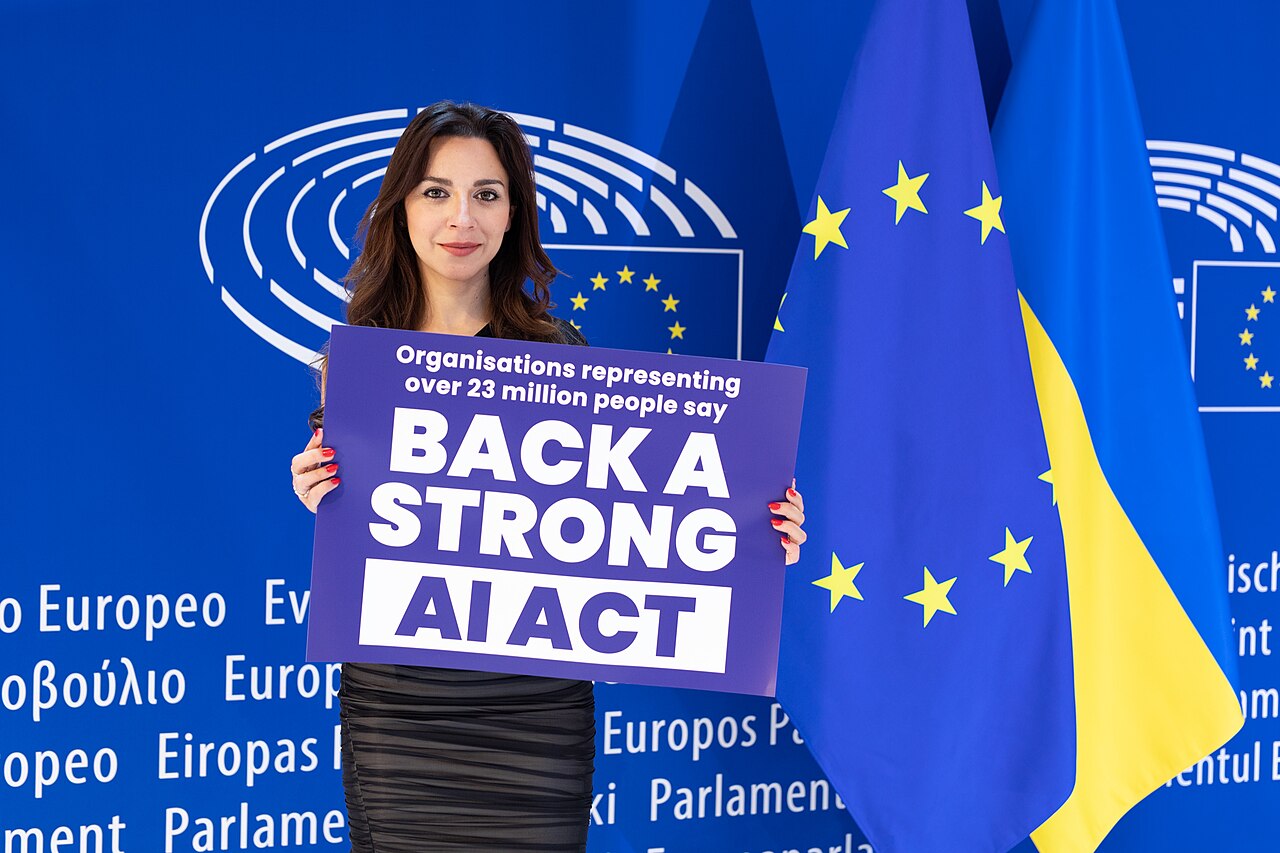
Commentary. Artificial intelligence policy is entering a more consequential phase. Regulators are no longer debating only hypothetical risks: banking authorities are examining whether AI-enabled cyberattacks or autonomous systems could threaten financial stability, while governments are building new oversight regimes for high-risk uses. Our view is straightforward: the public interest cannot be protected by voluntary promises alone, but blunt rules could also deprive society of useful technology.
The strongest argument for action is accountability. The Financial Stability Board’s October report recommends 12 practices for responsible AI adoption by financial institutions, including governance across the systems’ lifecycles. Reuters has reported that banking regulators are intensifying scrutiny amid concerns about cyberattacks and “rogue agents” that could destabilize banks. These developments point to a basic problem: when software can make decisions, act across networks and adapt faster than institutions can respond, someone must remain answerable for the consequences.
That principle should apply beyond finance. The European Commission has begun work on standards that help providers of high-risk systems demonstrate compliance with the EU AI Act, and Singapore’s financial regulator has issued AI risk-management guidelines for banks and other financial firms. Meanwhile, Canada and the United Kingdom have renewed cooperation on frontier-AI security, including technical evaluations and information sharing. The direction is clear: governments are moving toward documented testing, independent scrutiny and incident reporting rather than trusting assurances made behind closed doors.
Voluntary safeguards are not enough
Industry has a legitimate objection. AI companies argue that rapidly changing technology cannot be governed effectively by slow, prescriptive legislation. A rule written for today’s models may be obsolete before it takes effect. Smaller firms could face compliance costs that only the largest laboratories can absorb, reducing competition and concentrating power in the companies regulators are trying to supervise.
Those concerns deserve more than dismissal. A regulatory system that treats every application as equally dangerous would waste resources and discourage beneficial uses in medicine, education and scientific research. The United Kingdom’s debate over AI in healthcare illustrates the need for a framework that distinguishes medical devices and high-consequence decisions from ordinary productivity tools. Regulation should be proportionate, technically informed and revised through transparent evidence, not political fashion.
But flexibility is not the same as permission to self-police. The recent record of voluntary commitments is too thin a foundation for public trust. A pledge to use independent auditors is useful only if auditors are genuinely independent, their methods are disclosed and companies face consequences for withholding material findings. A promise to report incidents is meaningful only when reporting is mandatory, timely and protected from commercial retaliation.
What responsible rules should require
Our preferred approach is neither an AI moratorium nor a blank cheque. It is a tiered system built around consequences.
- High-risk systems should undergo independent testing before deployment and after major changes.
- Providers should report serious failures, unauthorized access and harmful autonomous behavior to a competent public authority.
- Organizations using AI should maintain clear human responsibility, audit trails and a practical way to suspend a system.
- Regulators should publish enough information for researchers and affected people to challenge unsafe outcomes without forcing companies to reveal legitimate trade secrets.
- Rules should be coordinated internationally where risks cross borders, especially in finance, cybersecurity and critical infrastructure.
This is not a demand for perfect foresight. It is a demand for institutional humility. No regulator, company or newsroom can know exactly how advanced systems will develop. That uncertainty makes testing and accountability more necessary, not less.
The political temptation will be to choose between acceleration and safety. That is a false choice. Innovation thrives when users can trust the systems placed in front of them, and trust depends on remedies when things go wrong. The public should not have to decide whether an AI failure was an unforeseeable accident or a foreseeable cost of doing business after the damage is done.
Our position is therefore modest but firm: let companies move quickly, but require them to leave evidence behind. Let governments avoid micromanaging technical design, but insist on independent checks, disclosure and human control where the stakes are high. The race for more capable AI may continue. The race to establish responsibility must not lag behind.
Sources
Reuters on banking regulators and AI stability risks; Financial Stability Board guidance on responsible AI adoption; Simmons & Simmons overview of October 2026 AI developments; Kepler privacy and cybersecurity update.