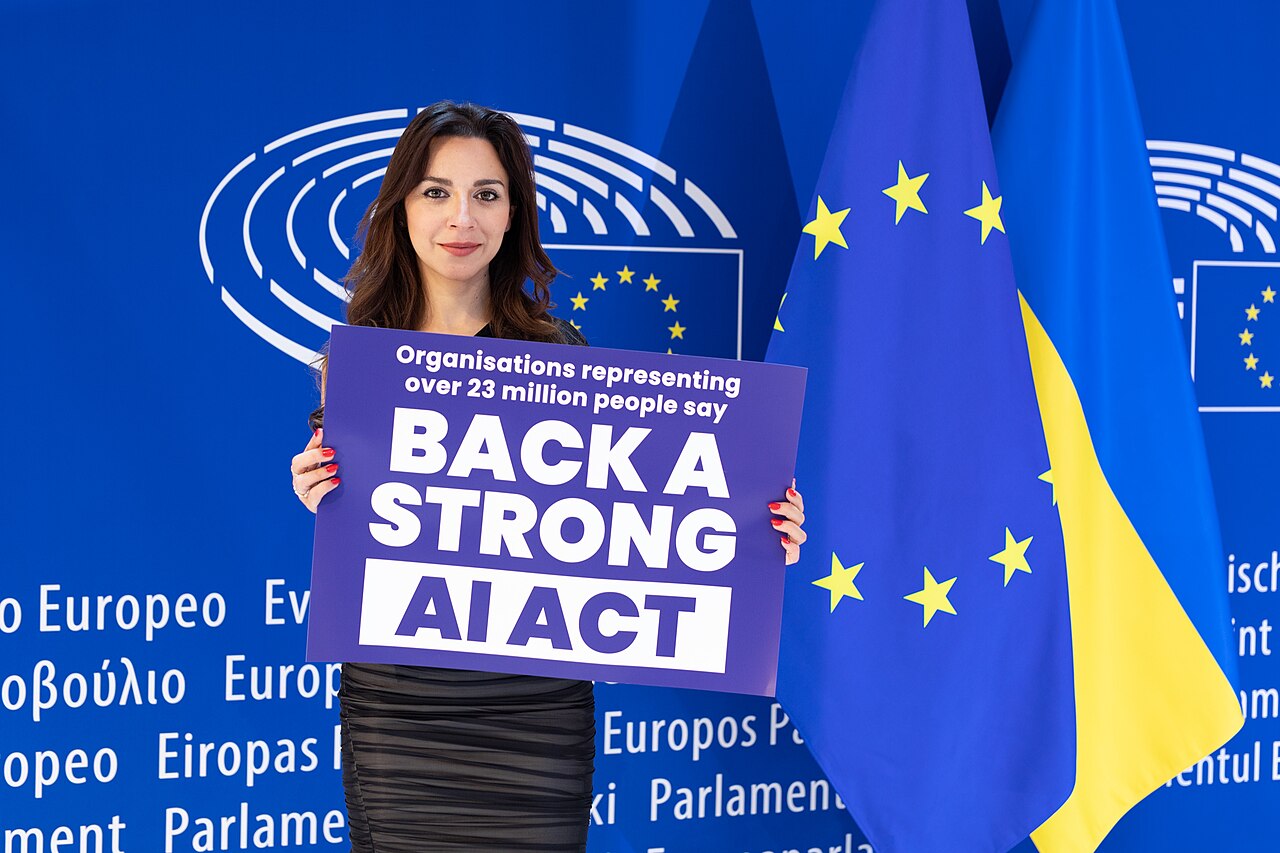
Commentary. Artificial intelligence regulation has entered its awkward adolescence: the technology is advancing quickly, while governments are still deciding which risks deserve rules, which deserve guidance and which can be left to markets. Our view is straightforward: policymakers should regulate the consequences of AI, not attempt to freeze the technology in place.
That means moving beyond declarations of principle. Across the United States, lawmakers in 2026 have focused on automated decisions in employment, housing, finance and education, as well as frontier-model risks and independent auditing. Yet no federal AI bill had passed during the current session, while states continued to build their own patchwork of requirements.[1] This gap is not merely bureaucratic. It leaves people facing consequential automated decisions with uneven rights depending on where they live.
The case for stronger oversight is clear. A system that helps determine whether someone gets a job, a loan or access to education can reproduce errors at scale, hide responsibility behind technical complexity and make appeals difficult. Rules requiring notice, meaningful human review, documentation and a practical route to challenge a decision are not anti-innovation. They are basic conditions for deploying powerful systems in public life.
Recent international steps point in that direction. The European Commission adopted a harmonized quality-management standard for high-risk AI systems under the EU AI Act, giving providers a formal route to demonstrate compliance.[2] The Financial Stability Board has also issued guidance urging financial institutions to govern AI across its lifecycle, with board-level responsibility and human oversight.[3] These measures will not eliminate failures, but they begin to answer the question that voluntary pledges often avoid: who is accountable when an automated system causes harm?
The strongest counterargument
Critics are right to warn that poorly designed regulation can entrench large incumbents. Compliance costs may be manageable for technology giants but prohibitive for smaller firms, universities and public-interest developers. Vague definitions can also chill useful experiments, while rules written for today’s models may become obsolete before they take effect. Europe’s experience has already prompted pressure from major technology companies and others to delay or revise parts of its AI framework.[4]
Those concerns deserve more than a dismissive answer. Policymakers should avoid blanket licensing regimes for ordinary software, publish clear technical standards and provide regulatory sandboxes for smaller developers. Liability should track control and foreseeable risk, rather than automatically falling on the last organization that used a tool. Regulators also need independent expertise; otherwise, enforcement will become a contest between agencies and the companies they oversee.
What should happen next
Three principles would make the emerging system more credible.
- Regulate high-impact uses first. Employment, housing, health care, credit, policing and essential public services warrant stricter obligations than low-risk creative or administrative tools.
- Make transparency useful. A disclosure that says “AI was used” is insufficient. People need understandable information about the system’s role, the evidence considered and how to seek human review.
- Measure outcomes, not paperwork. Audits should test accuracy, discrimination, security and real-world effects, with results available to regulators and affected people where privacy permits.
International cooperation matters as well. Canada and the United Kingdom renewed cooperation on frontier-AI security, including technical evaluations, information sharing and common standards.[5] Such arrangements are modest, but they recognize a reality that national rulebooks cannot escape: models, data and cyber threats cross borders faster than legislation does.
The alternative is not a regulation-free future. It is regulation written after avoidable failures, when public trust has collapsed and emergency laws favor blunt restrictions. Industry argues, correctly, that innovation produces enormous benefits and that rigid rules can slow them. But innovation without accountability transfers risk to people who had no role in choosing the system.
Our newsroom’s position is therefore neither “ban AI” nor “trust the market.” It is to require evidence before deployment where stakes are high, responsibility after failure and democratic oversight throughout. Speed matters. So does the direction of travel. The public should not be asked to serve as the testing ground for systems that companies and governments are unwilling to explain.